
Security Awareness
Third-Party Breach Risk
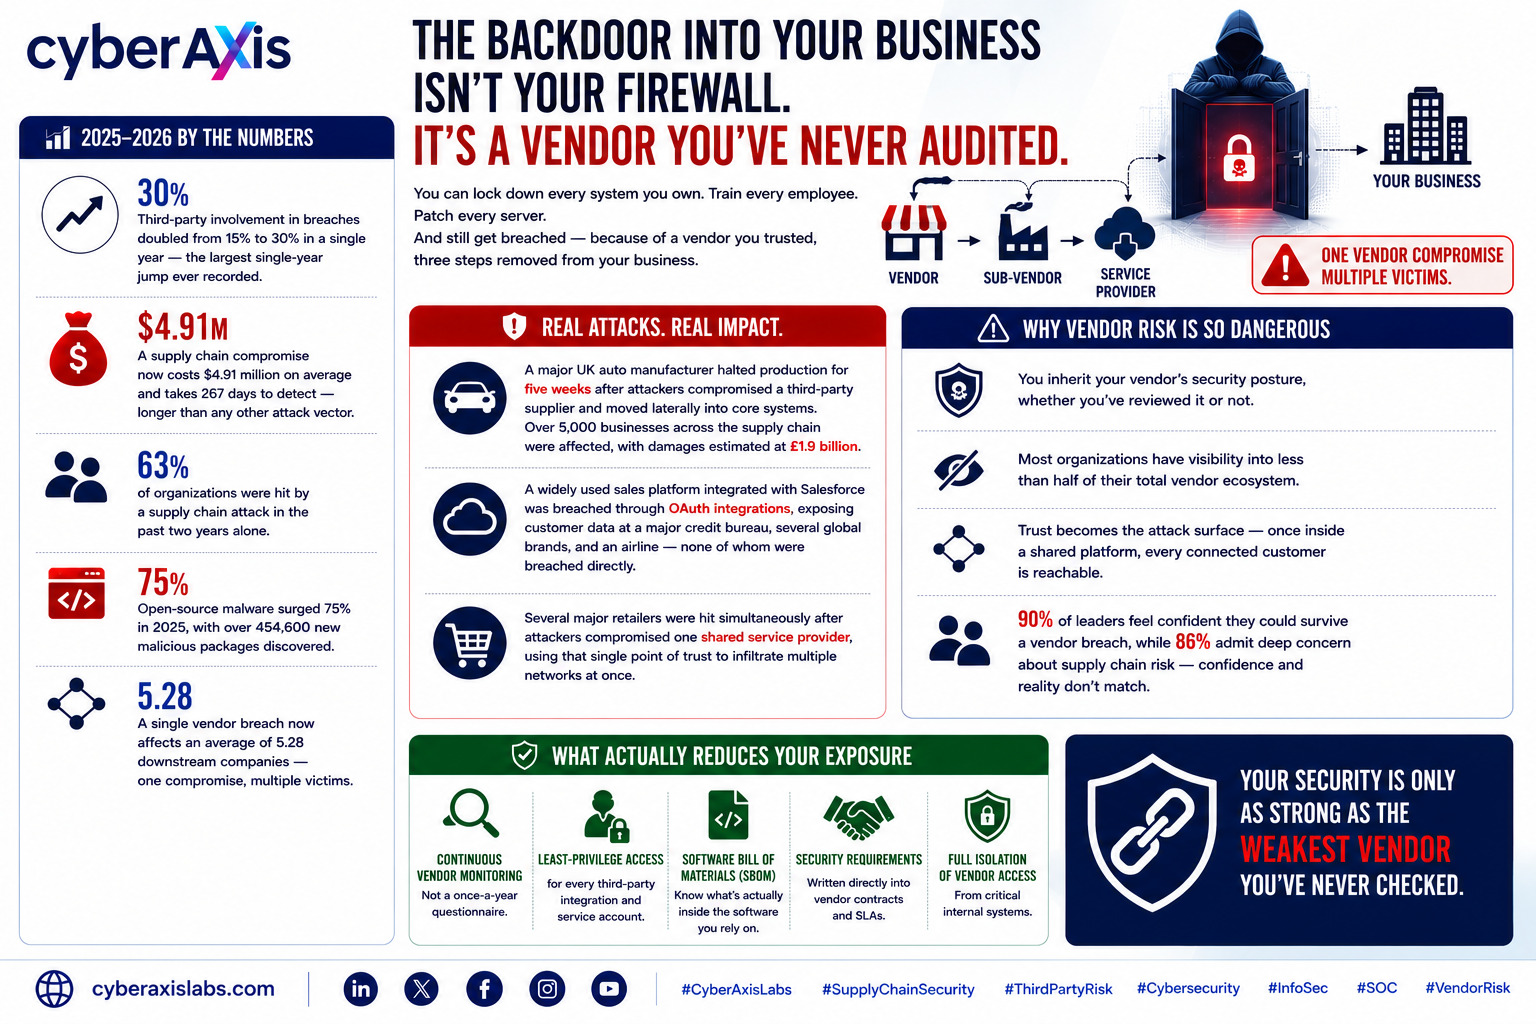
The Backdoor Into Your Business Isn't Your Firewall. It's a Vendor You've Never Audited.
You can lock down every system you own. Train every employee. Patch every server.
And still get breached — because of a vendor you trusted, three steps removed from your business.
Here's what 2025-2026 looked like:
→ Third-party involvement in breaches doubled from 15% to 30% in a single year — the largest single-year jump ever recorded
→ A supply chain compromise now costs $4.91 million on average and takes 267 days to detect — longer than any other attack vector
→ 63% of organizations were hit by a supply chain attack in the past two years alone
→ Open-source malware surged 75% in 2025, with over 454,600 new malicious packages discovered
→ A single vendor breach now affects an average of 5.28 downstream companies — one compromise, multiple victims
Real attacks that started with a vendor, not a direct breach:
A major UK auto manufacturer halted production for five weeks after attackers compromised a third-party supplier and moved laterally into core systems. Over 5,000 businesses across the supply chain were affected, with damages estimated at £1.9 billion.
A widely used sales platform integrated with Salesforce was breached through OAuth integrations, exposing customer data at a major credit bureau, several global brands, and an airline — none of whom were breached directly.
Several major retailers were hit simultaneously after attackers compromised one shared service provider, using that single point of trust to infiltrate multiple networks at once.
Why vendor risk is so dangerous:
- You inherit your vendor's security posture, whether you've reviewed it or not
- Most organizations have visibility into less than half of their total vendor ecosystem
- Trust becomes the attack surface — once inside a shared platform, every connected customer is reachable
- 90% of leaders feel confident they could survive a vendor breach, while 86% admit deep concern about supply chain risk — confidence and reality don't match
What actually reduces your exposure:
→ Continuous vendor monitoring — not a once-a-year questionnaire→ Least-privilege access for every third-party integration and service account
→ Software Bill of Materials (SBOM) — know what's actually inside the software you rely on
→ Security requirements written directly into vendor contracts and SLAs
→ Full isolation of vendor access from critical internal systems
Your security is only as strong as the weakest vendor you've never checked.
cyberaxislabs.com
#CyberAxisLabs #SupplyChainSecurity #ThirdPartyRisk #Cybersecurity #InfoSec #SOC #VendorRisk
We appreciate your feedback - share your comments at [email protected]
Comments 0
Email-verified comments are reviewed before they are published.