
Security Awareness
MFA: Why It Matters
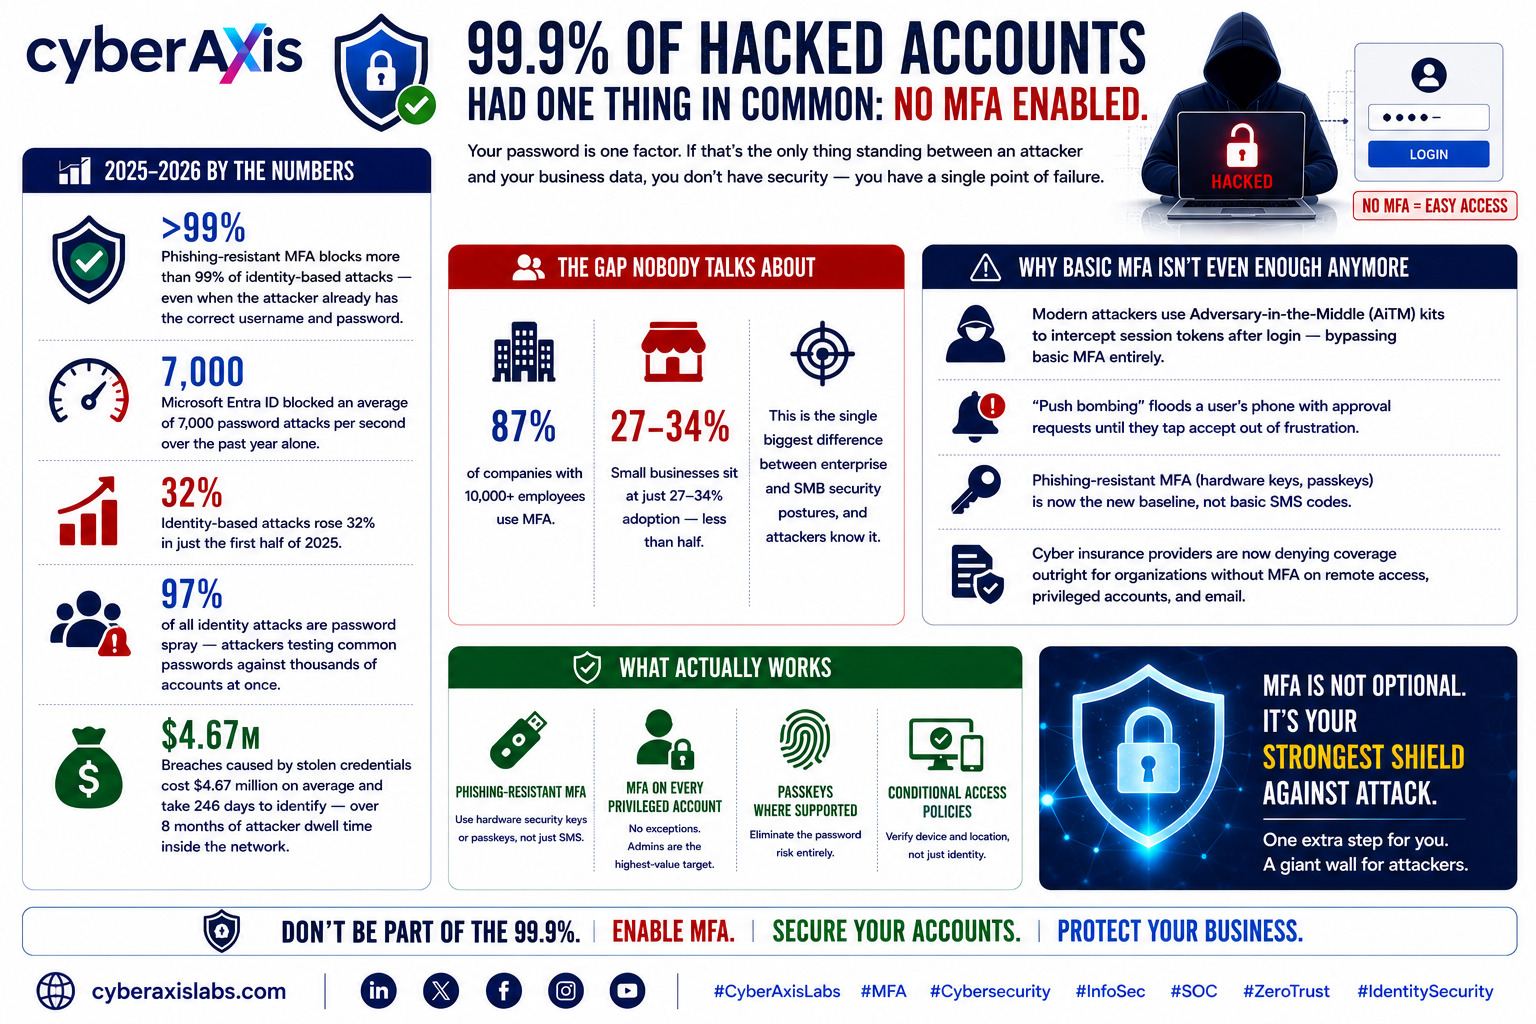
99.9% of Hacked Accounts Had One Thing in Common: No MFA Enabled.
Your password is one factor.If that's the only thing standing between an attacker and your business data, you don't have security — you have a single point of failure.
Here's what 2025-2026 looked like:
→ Phishing-resistant MFA blocks more than 99% of identity-based attacks — even when the attacker already has the correct username and password
→ Microsoft Entra ID blocked an average of 7,000 password attacks per second over the past year alone
→ Identity-based attacks rose 32% in just the first half of 2025
→ 97% of all identity attacks are password spray — attackers testing common passwords against thousands of accounts at once
→ Breaches caused by stolen credentials cost $4.67 million on average and take 246 days to identify — over 8 months of attacker dwell time inside the network
The gap nobody talks about:
→ 87% of companies with 10,000+ employees use MFA
→ Small businesses sit at just 27-34% adoption — less than half
→ This is the single biggest difference between enterprise and SMB security postures, and attackers know it
Why basic MFA isn't even enough anymore:
✦ Modern attackers use Adversary-in-the-Middle (AiTM) kits to intercept session tokens after login — bypassing basic MFA entirely
✦ "Push bombing" floods a user's phone with approval requests until they tap accept out of frustration
✦ Phishing-resistant MFA (hardware keys, passkeys) is now the new baseline, not basic SMS codes
✦ Cyber insurance providers are now denying coverage outright for organizations without MFA on remote access, privileged accounts, and email
What actually works:
→ Phishing-resistant MFA — hardware security keys or passkeys, not just SMS
→ MFA on every privileged account, no exceptions — admins are the highest-value target
→ Passkeys where supported — eliminates the password risk entirely
→ Conditional access policies — verify device and location, not just identity
cyberaxislabs.com
#CyberAxisLabs #MFA #Cybersecurity #InfoSec #SOC #ZeroTrust #IdentitySecurity
We appreciate your feedback - share your comments at [email protected]
Comments 0
Email-verified comments are reviewed before they are published.