
Malware Strikes Silently
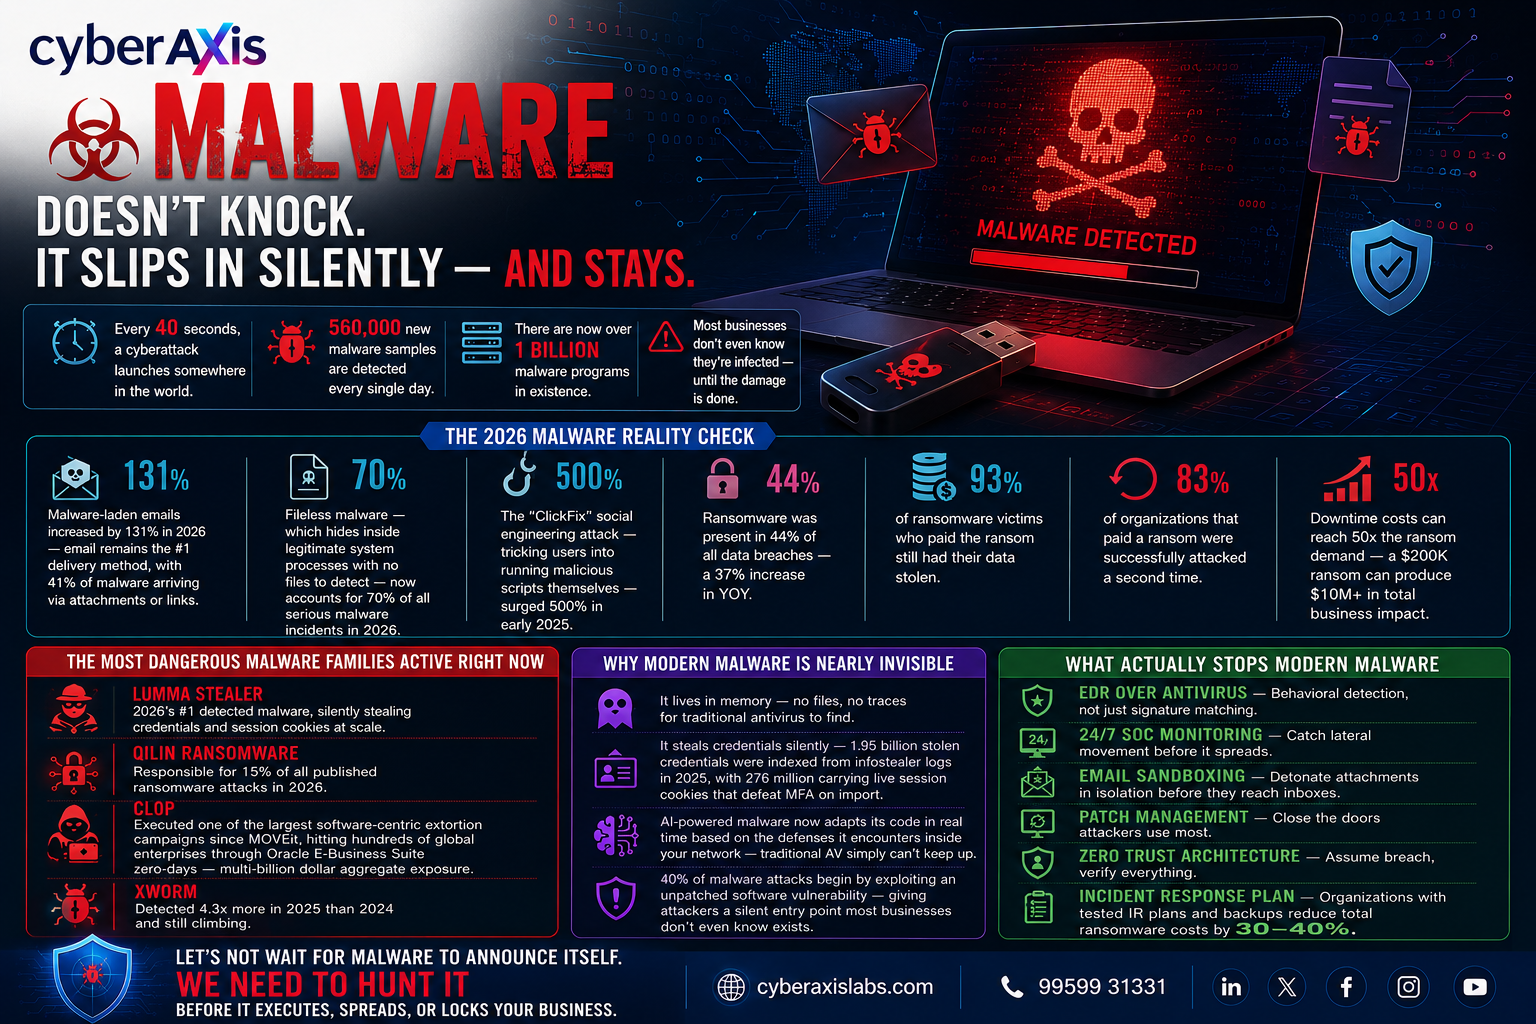
Malware Doesn't Knock. It Slips In Silently — And Stays.
Every 40 seconds, a cyberattack launches somewhere in the world.
Most of them start with malware.
560,000 new malware samples are detected every single day.
There are now over 1 billion malware programs in existence.
And the worst part? Most businesses don't even know they're infected — until the damage is done.
The 2026 Malware Reality Check:
→ Malware-laden emails increased by 131% in 2026 — email remains the #1 delivery method, with 41% of malware arriving via attachments or links
→ Fileless malware — which hides inside legitimate system processes with no files to detect — now accounts for 70% of all serious malware incidents in 2026
→ The "ClickFix" social engineering attack — tricking users into running malicious scripts themselves — surged 500% in early 2025
→ Ransomware was present in 44% of all data breaches — a 37% increase in YOY
→ 93% of ransomware victims who paid the ransom still had their data stolen
→ 83% of organizations that paid a ransom were successfully attacked a second time
→ Downtime costs can reach 50x the ransom demand — a $200K ransom can produce $10M+ in total business impact
The Most Dangerous Malware Families Active Right Now:
Lumma Stealer — 2026's #1 detected malware, silently stealing credentials and session cookies at scale
Qilin Ransomware — responsible for 15% of all published ransomware attacks in 2026
Cl0p — executed one of the largest software-centric extortion campaigns since MOVEit, hitting hundreds of global enterprises through Oracle E-Business Suite zero-days — multi-billion dollar aggregate exposure
XWorm — detected 4.3x more in 2025 than 2024 and still climbing
Why modern malware is nearly invisible:
✦ It lives in memory — no files, no traces for traditional antivirus to find
✦ It steals credentials silently — 1.95 billion stolen credentials were indexed from infostealer logs in 2025, with 276 million carrying live session cookies that defeat MFA on import
✦ AI-powered malware now adapts its code in real time based on the defenses it encounters inside your network — traditional AV simply can't keep up
✦ 40% of malware attacks begin by exploiting an unpatched software vulnerability — giving attackers a silent entry point most businesses don't even know exists
What actually stops modern malware:
→ EDR over Antivirus — behavioral detection, not just signature matching
→ 24/7 SOC Monitoring — catch lateral movement before it spreads
→ Email Sandboxing — detonate attachments in isolation before they reach inboxes
→ Patch Management — close the doors attackers use most
→ Zero Trust Architecture — assume breach, verify everything
→ Incident Response Plan — organizations with tested IR plans and backups reduce total ransomware costs by 30–40%
Lets don't wait for malware to announce itself, we need to hunt it before it executes, spreads, or locks your business.
#CyberAxisLabs #Malware #Ransomware #Cybersecurity #InfoSec #SOC #EDR
We appreciate your feedback - share your comments at [email protected]
Comments 0
Email-verified comments are reviewed before they are published.