
Cybersecurity
Credential Stuffing Exposed
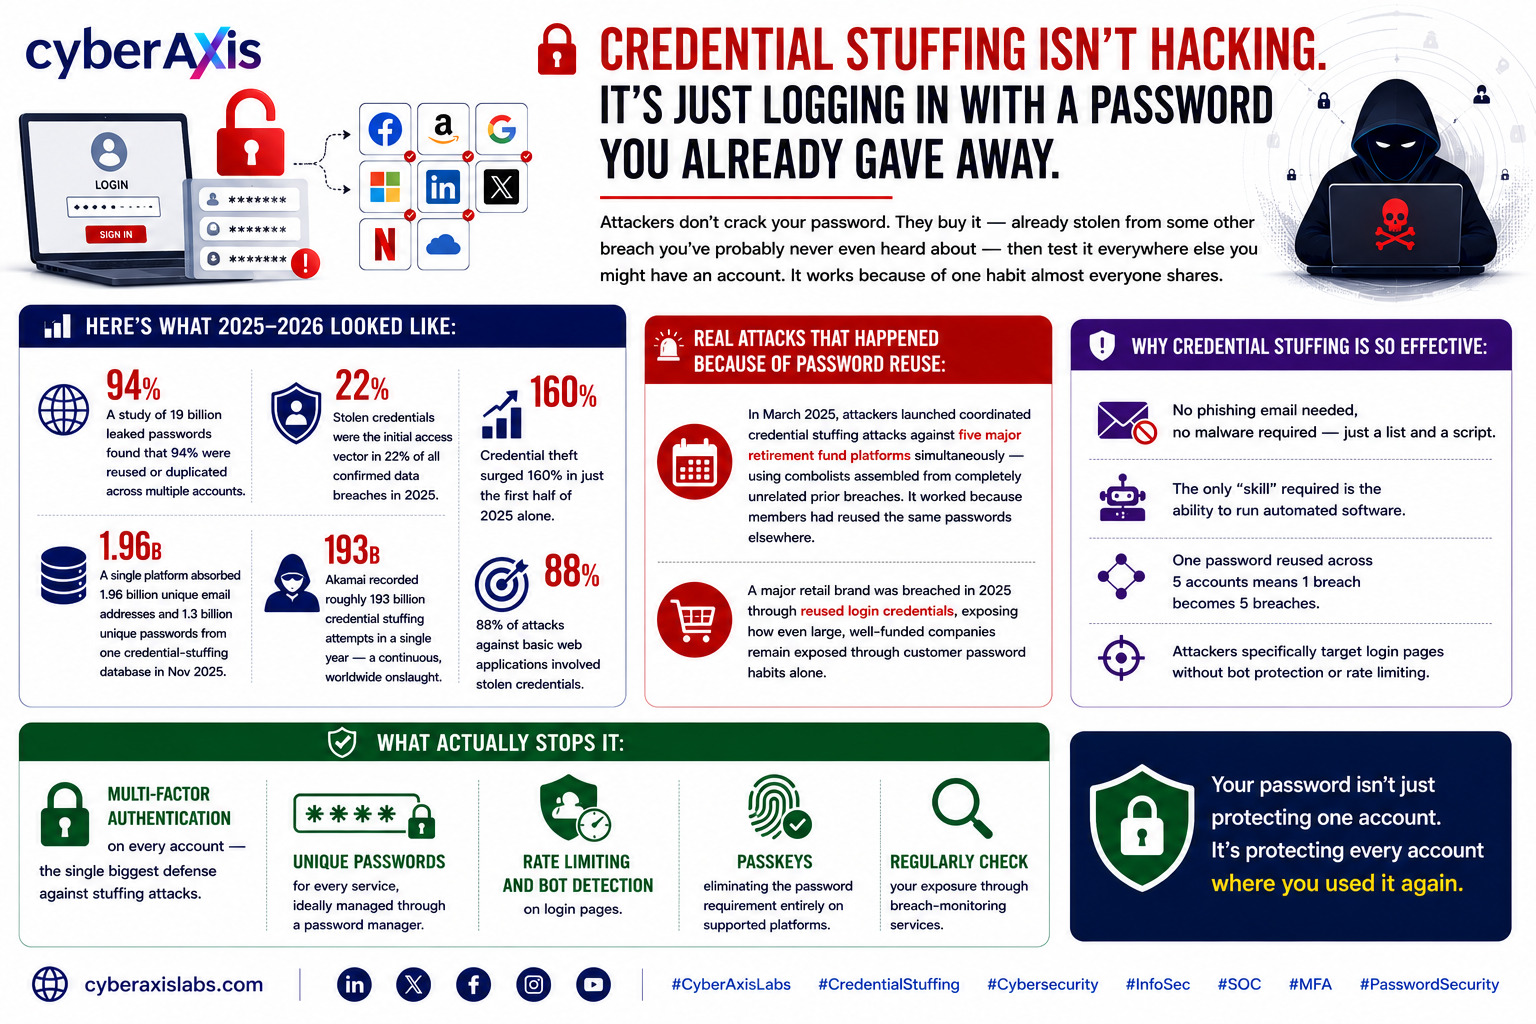
Credential Stuffing Isn't Hacking. It's Just Logging In With a Password You Already Gave Away.
Attackers don't crack your password. They buy it — already stolen from some other breach you've probably never even heard about — then test it everywhere else you might have an account.
It works because of one habit almost everyone shares.
Here's what 2025-2026 looked like:
→ A study of 19 billion leaked passwords found that 94% were reused or duplicated across multiple accounts→ Stolen credentials were the initial access vector in 22% of all confirmed data breaches in 2025
→ Credential theft surged 160% in just the first half of 2025 alone
→ A single platform absorbed 1.96 billion unique email addresses and 1.3 billion unique passwords from one credential-stuffing database in November 2025
→ Akamai recorded roughly 193 billion credential stuffing attempts in a single year — a continuous, worldwide onslaught
→ 88% of attacks against basic web applications involved stolen credentials
Real attacks that happened because of password reuse:
In March 2025, attackers launched coordinated credential stuffing attacks against five major retirement fund platforms simultaneously — using combolists assembled from completely unrelated prior breaches. It worked because members had reused the same passwords elsewhere.A major retail brand was breached in 2025 through reused login credentials, exposing how even large, well-funded companies remain exposed through customer password habits alone.
Why credential stuffing is so effective:
✦ No phishing email needed, no malware required — just a list and a script✦ The only "skill" required is the ability to run automated software
✦ One password reused across 5 accounts means 1 breach becomes 5 breaches
✦ Attackers specifically target login pages without bot protection or rate limiting
What actually stops it:
→ Multi-Factor Authentication on every account — the single biggest defense against stuffing attacks→ Unique passwords for every service, ideally managed through a password manager
→ Rate limiting and bot detection on login pages
→ Passkeys — eliminating the password requirement entirely on supported platforms
→ Regularly checking your exposure through breach-monitoring services
Your password isn't just protecting one account. It's protecting every account where you used it again.
cyberaxislabs.com
#CyberAxisLabs #CredentialStuffing #Cybersecurity #InfoSec #SOC #MFA #PasswordSecurity
We appreciate your feedback - share your comments at [email protected]
Comments 0
Email-verified comments are reviewed before they are published.