
SMB Cyber Risks 2026
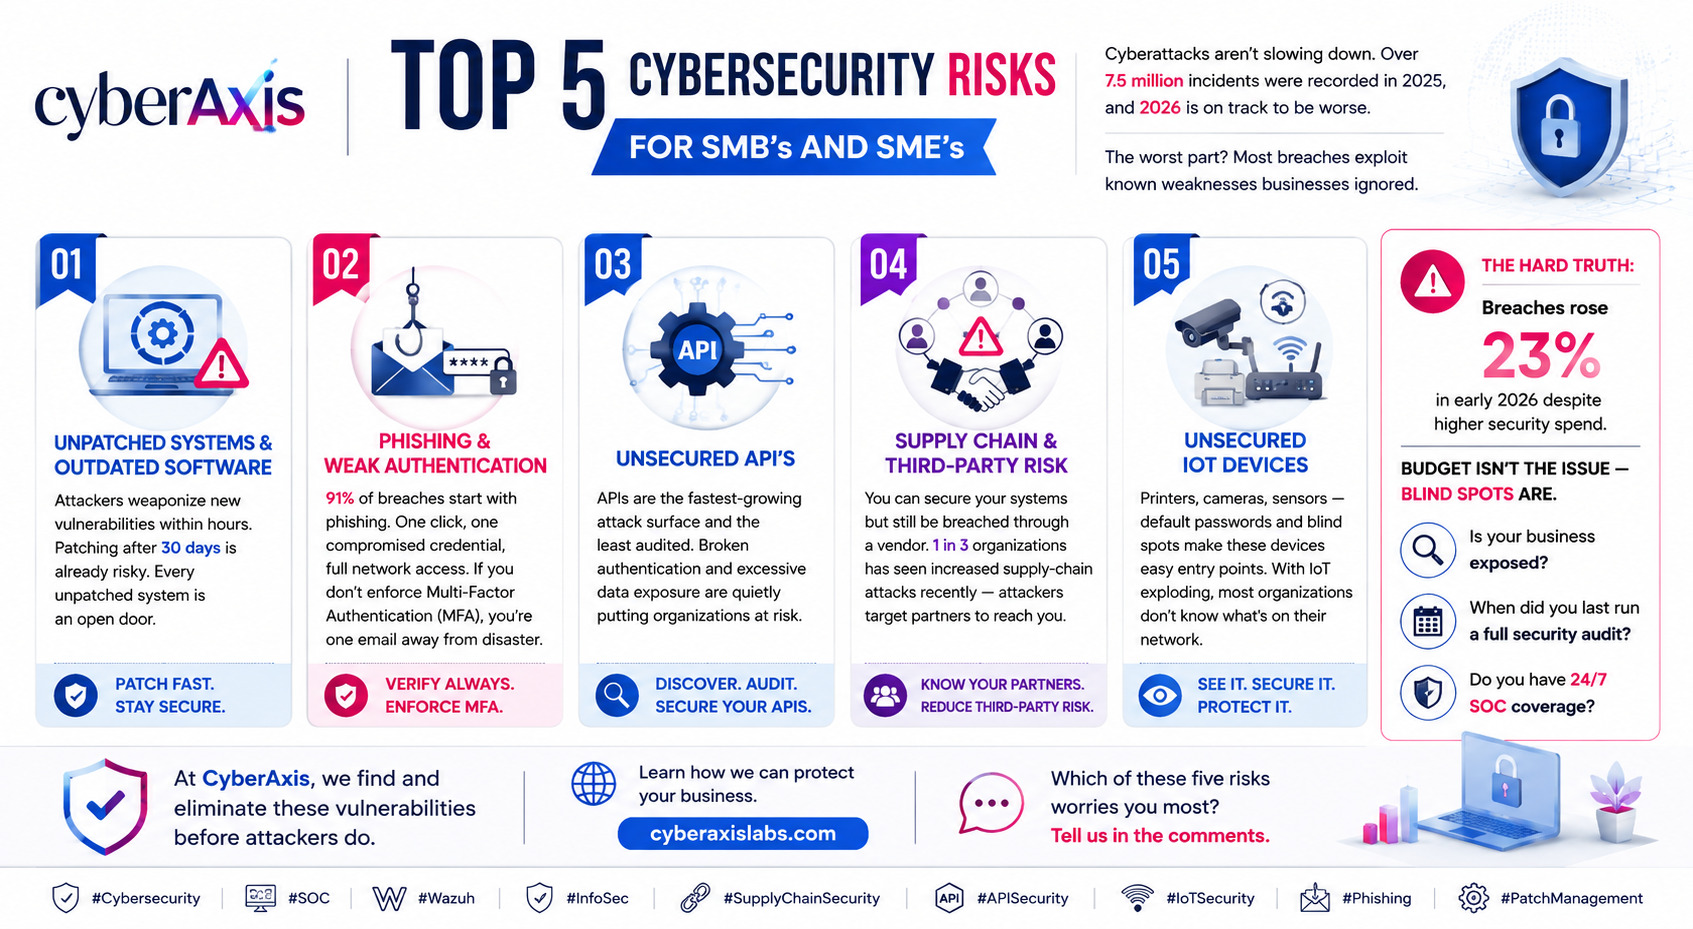
Top 5 Cybersecurity Risks for SMB's and SME's
Cyberattacks aren’t slowing down. Over 7.5 million incidents were recorded in 2025, and 2026 is on track to be worse. The worst part? Most breaches exploit known weaknesses businesses ignored.
1. Unpatched Systems & Outdated Software
Attackers weaponize new vulnerabilities within hours. Patching after 30 days is already risky. Every unpatched system is an open door.
2. Phishing & Weak Authentication
91% of breaches start with phishing. One click, one compromised credential, full network access. If you don’t enforce Multi-Factor Authentication (MFA), you’re one email away from disaster.
3. Unsecured APIs
APIs are the fastest-growing attack surface and the least audited. Broken authentication and excessive data exposure are quietly putting organizations at risk.
4. Supply Chain & Third-Party Risk
You can secure your systems but still be breached through a vendor. 1 in 3 organizations has seen increased supply-chain attacks recently — attackers target partners to reach you.
5. Unsecured IoT Devices
Printers, cameras, sensors — default passwords and blind spots make these devices easy entry points. With IoT exploding, most organizations don’t know what’s on their network.
The hard truth: breaches rose 23% in early 2026 despite higher security spend. Budget isn’t the issue — blind spots are.
Is your business exposed? When did you last run a full security audit? Do you have 24/7 SOC coverage?
At CyberAxis Labs, we find and eliminate these vulnerabilities before attackers do.
cyberaxislabs.com
Which of these five risks worries you most? Tell us in the comments.
#CyberAxisLabs #Cybersecurity #SOC #Wazuh #InfoSec #SupplyChainSecurity #APISecurity #IoTSecurity #Phishing #PatchManagement
We appreciate your feedback - share your comments at [email protected]
Comments 0
Email-verified comments are reviewed before they are published.